
Demo Application
Open the Demo Application
Section titled “Open the Demo Application”For the AWS reference deployment, navigate to https://client-side-defense.f5-sales-demo.com. This
is the Juice Shop application protected by the F5 Distributed Cloud HTTP load balancer. The Azure
third-party lifecycle is a separate full-origin scenario deployed from the
webapp-api-protection repository; use
that deployment’s LB_FQDN output instead of the AWS hostname. The Azure application and its
separately deployed cdn-simulator remain owned by their respective repositories, backends, and
saved plans. Do not manage or tear down those Azure-owned resources through this repository’s
terraform/aws stack or standalone CSD API workflow.
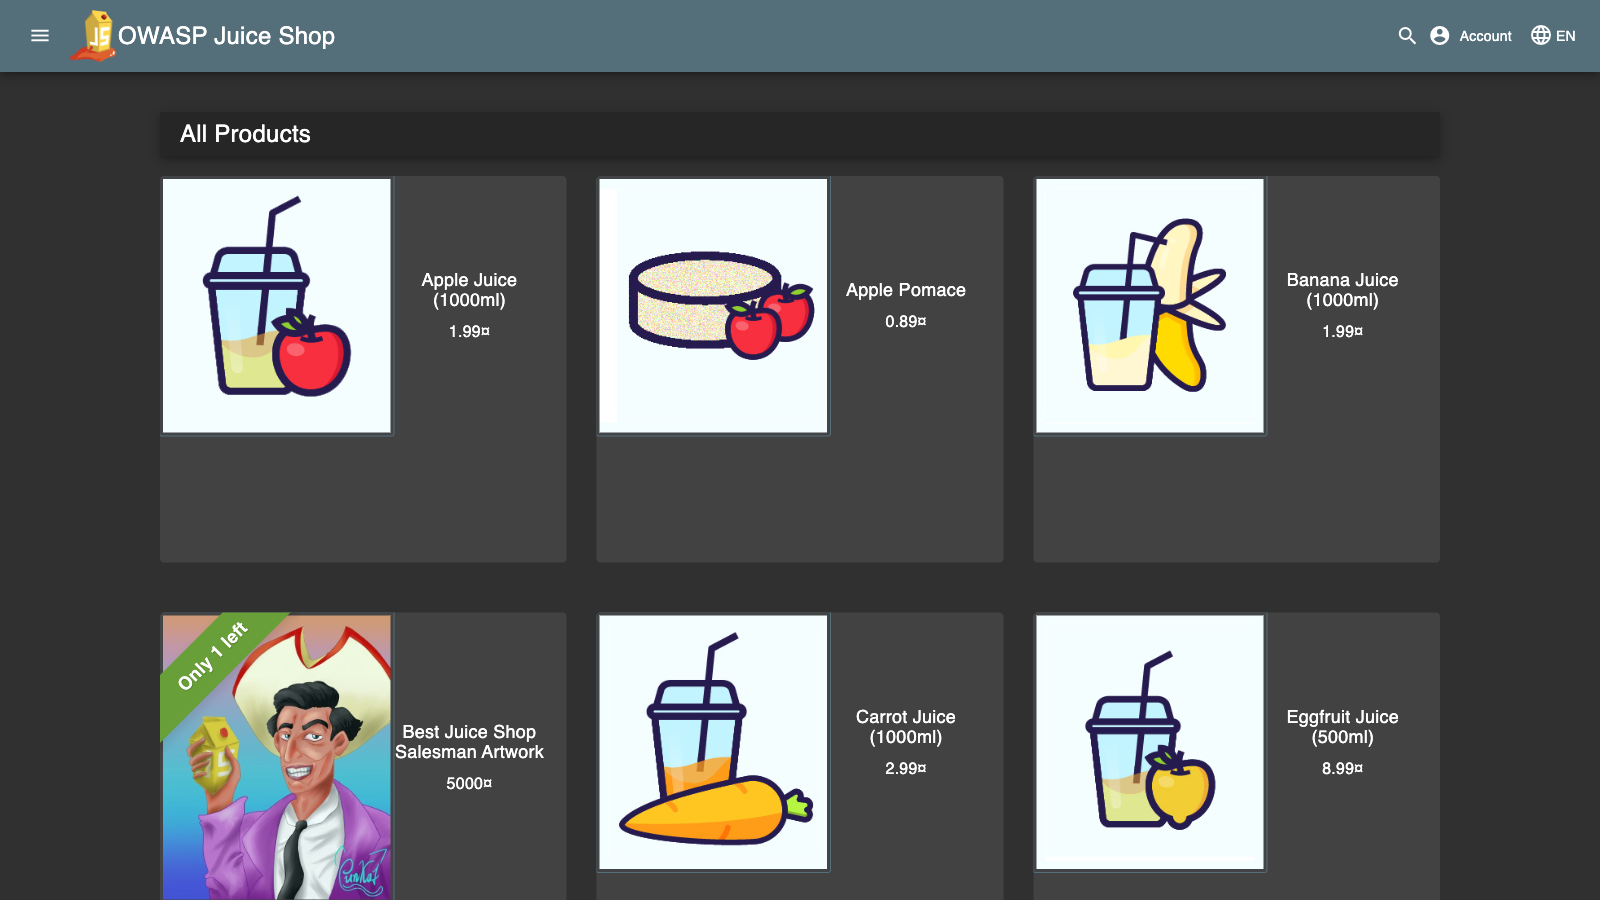
UI-layout example only. Labels and styling may differ from the current deployed application.
Review Pages with Form Inputs
Section titled “Review Pages with Form Inputs”The login page is the primary page used in the AWS Juice Shop demo:
- Navigate to the Login page (
/#/login).
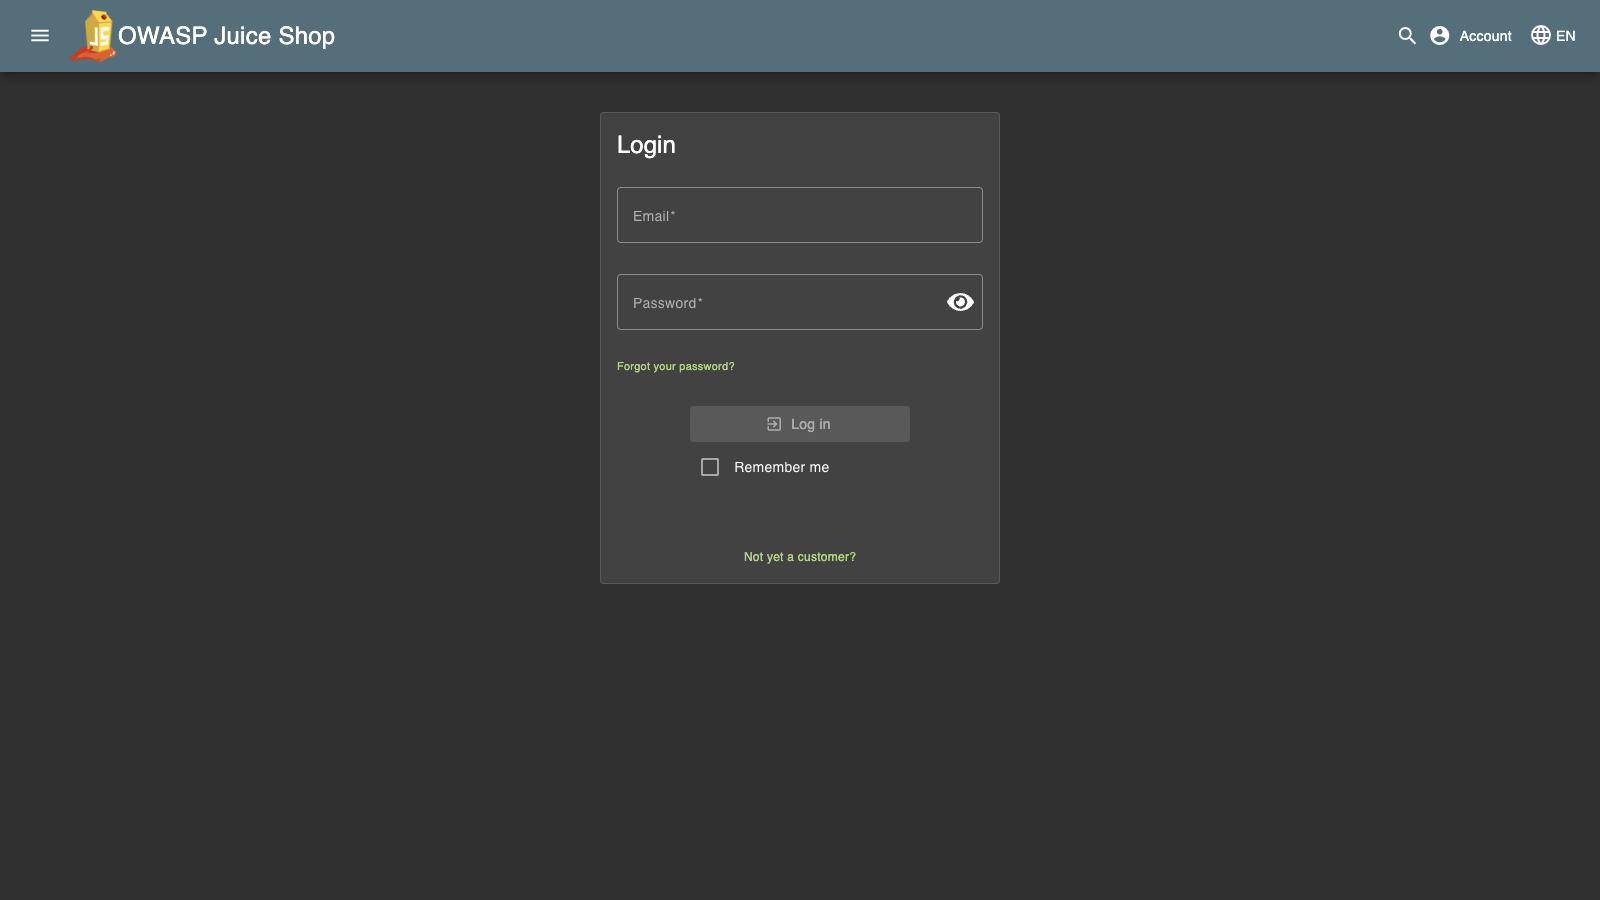
UI-layout example only. Labels and styling may differ from the current deployed application.
CSD auto-classifies the email and password fields as sensitive, making this page ideal for demonstrating formjacking detection. The Trigger Detection section uses this page.
The AWS Juice Shop application has additional pages with form inputs that CSD monitors. Each route
below is relative to https://client-side-defense.f5-sales-demo.com and collects data that a
formjacking script could exfiltrate:
| Page | Route | Sensitive Fields | Data Category |
|---|---|---|---|
| Registration | /#/register | email, password, security question & answer | Credentials, account recovery |
| Forgot Password | /#/forgot-password | email, security answer, new password | Credentials |
| Payment | /#/payment/shop | cardholder name, card number, expiry | Financial |
| Address | /#/address/create | name, mobile number, address, city, ZIP code, country | PII |
| Contact | /#/contact | author, comment | PII |
| Complaint | /#/complain | email, message, file upload | PII |
| Change Password | /#/privacy-security/change-password | current password, new password | Credentials |
CSD monitors all pages where JavaScript injection is enabled — not just those listed above.